
Here’s the thing about Mac malware: the scariest thing you’ll see on your screen almost certainly isn’t malware. It’s an ad. A flashing red box saying “APPLE SECURITY ALERT: 3 VIRUSES DETECTED” is a web page, not a diagnosis, and it has no idea what’s on your Mac.
Meanwhile, actual macOS malware does exist in 2026, it’s more common than it was five years ago, and it looks nothing like that popup. It’s quiet, it arrives as something you chose to install, and its goal is your passwords and crypto wallets.
The quick answer: Almost every “your Mac is infected” warning is a scam ad in your browser. Close the tab; don’t call the number, don’t download the “fix.” Real Mac malware in 2026 is mostly infostealers and adware that arrive when you install something: a fake app installer, a “codec” or “Flash update,” a bogus meeting app from a fake recruiter, or a Terminal command someone talked you into pasting. macOS already ships with defenses: Gatekeeper checks signatures, XProtect blocks known malware, and notarization vets most software. Your real job is to stop installing untrusted things, audit your login items and configuration profiles, and remove anything you don’t recognize. Most paid “Mac cleaner” apps are aggressive junkware that create the problem they claim to solve. You almost certainly do not need to buy anything.
Why the popups are fake, and how to be sure
A web page cannot scan your file system. That’s not a policy, it’s a hard boundary in how browsers work. So any page claiming to have found viruses on your Mac is lying by definition. These ads use a few reliable tells:
- They appear inside a browser window, often in a tab you didn’t open
- They use Apple logos and system-looking fonts, but the design is slightly off
- There’s a countdown timer, or a phone number to call “Apple Support”
- Clicking anywhere, including the X, triggers a download
- The page tries to block you from leaving with an endless dialog
To get out safely: don’t click inside the page. Use Cmd+W to close the tab, or right-click the Safari or Chrome icon in the Dock and choose Quit. If the page won’t let go, force quit the browser with Cmd+Option+Esc. Then reopen it and do not restore the previous session.
Genuine macOS warnings look boring. They’re small gray system dialogs, they don’t have logos, and they never ask you to call anyone. Apple does not cold-call you and does not put phone numbers in security alerts.
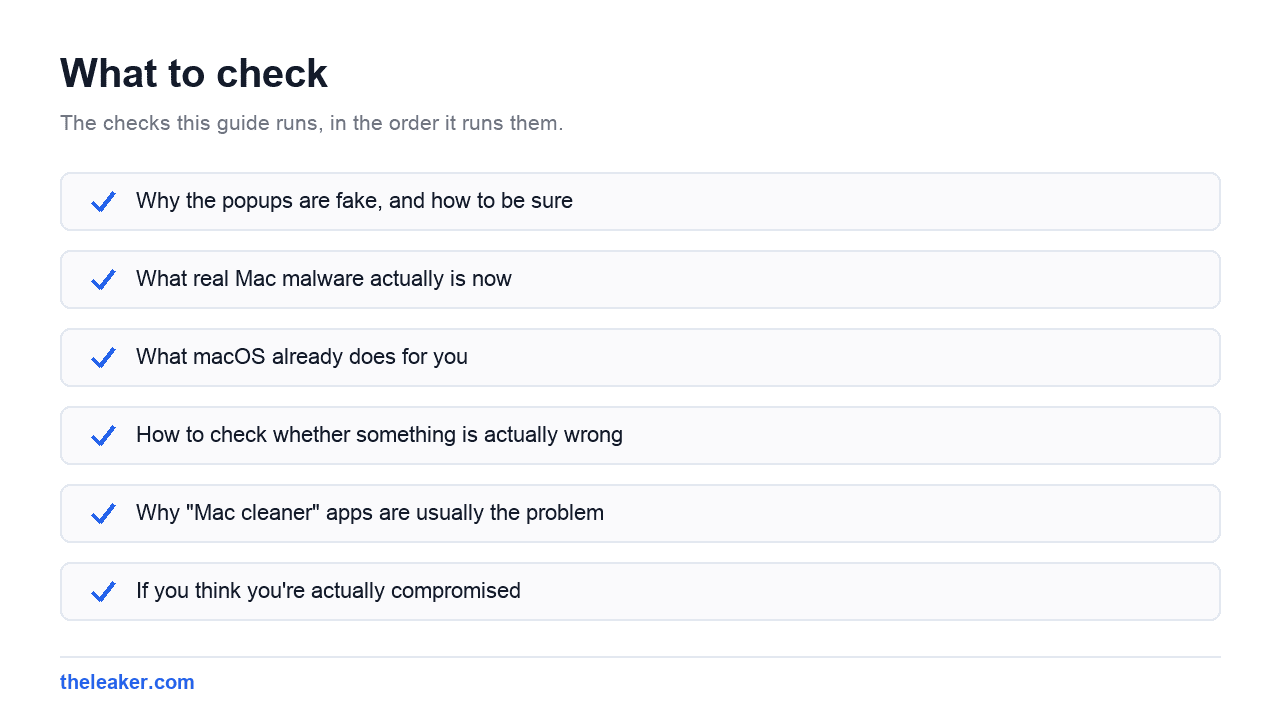
What real Mac malware actually is now
The threat landscape shifted. Old-style viruses that spread on their own are essentially nonexistent on macOS. What security researchers actually see today falls into three buckets.
Infostealers
This is the dominant category and it grew fast. These are programs designed to grab everything valuable in one pass: browser-saved passwords, session cookies, keychain contents, crypto wallet files, and any documents that look like credentials. Microsoft’s security team and Palo Alto Networks’ Unit 42 have both published research through 2025 and 2026 documenting a steady rise in macOS-targeted stealers, including families like Atomic macOS Stealer, and noting that some variants are updated specifically to slip past Apple’s XProtect signatures.
They typically arrive one of two ways. Either you download a cracked or “free” version of paid software from a sketchy site, which is the single most common infection path and a very good reason not to do that, or you get socially engineered into pasting a command into Terminal. That second one, often called ClickFix, is worth internalizing: a page tells you to “verify you’re human” or “fix a display error” by copying a line and running it in Terminal. Microsoft documented campaigns using exactly this lure against Mac users in 2026. Never paste a command into Terminal because a website told you to. Never.
Adware and browser hijackers
The old classics: things that change your search engine, inject ads, or install a browser extension you never asked for. Usually bundled with “free download manager” style apps or fake media players. Annoying rather than catastrophic, but they persist through login items and profiles.
Targeted spyware
Real, but not aimed at you. Commercial surveillance tools do target macOS and iOS, and Apple sends notifications to people it believes are targeted. If you’re a journalist, activist, or in a similarly exposed role, look at macOS Lockdown Mode. If you’re not, this isn’t your threat model.
What macOS already does for you
Gatekeeper checks that an app is signed by an identified developer and, for most software, notarized by Apple before it will open. When you see “cannot be opened because it is from an unidentified developer,” that’s Gatekeeper doing its job. The right-click-and-Open workaround exists, and every piece of malware’s instructions tell you to use it. Think hard before you do.
XProtect is the built-in signature scanner. It updates silently in the background, separately from macOS releases, and blocks known malware families on launch. It isn’t perfect (researchers regularly document stealer variants that evade current signatures), but it’s a real layer and it costs you nothing.
Notarization means Apple has automatically scanned a developer’s app for known malicious content. Not a guarantee of quality, but it’s a meaningful filter.
System Integrity Protection keeps even an administrator from modifying protected system files. Combined with app sandboxing and per-app permission prompts for your camera, microphone, screen, and Documents folder, the modern Mac is genuinely hard to quietly compromise, unless you personally approve it. Which is the whole game.
How to check whether something is actually wrong
Do this in order. It takes about ten minutes and it’s how professionals would start.
1. Check your login items
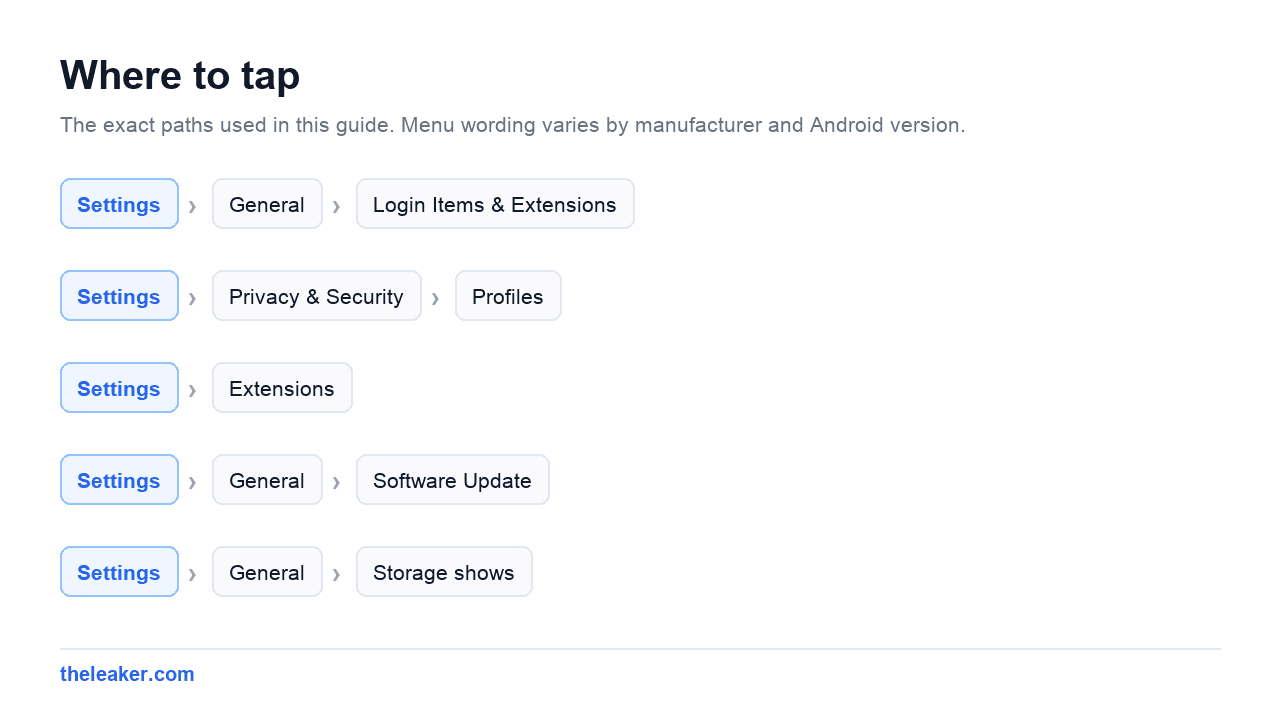
System Settings → General → Login Items & Extensions. You’ll see two lists: apps that open at login, and “Allow in the Background”: background helpers registered by installed software. Read every entry. Legitimate ones are usually named after apps you recognize (Dropbox, Google, your VPN, a printer driver). Anything with a nonsense name, a generic name like “MacUpdater Helper,” or a developer you don’t recognize is worth investigating. Toggle it off first, restart, and see if anything breaks before deleting the app.
2. Check configuration profiles
System Settings → Privacy & Security → Profiles. On a personal Mac that isn’t managed by an employer or school, this section should be empty, and if the item doesn’t appear at all, that means you have none, which is good. A profile you didn’t install is a serious red flag: adware uses them to lock your browser’s homepage and search engine so you can’t change them back. Remove any you don’t recognize.
3. Check browser extensions
Safari → Settings → Extensions, and the equivalent in Chrome, Edge, or Firefox. Remove anything you didn’t deliberately install. Extensions are the highest-leverage attack surface on any computer, because they can read every page you visit.
4. Look at Activity Monitor, but calmly
Sort by CPU. If something is pinning a core while your Mac is idle, look up the process name. Be warned: most of the alarming-looking names in Activity Monitor are normal macOS processes with cryptic names. Search before you panic, and don’t force-quit things you can’t identify.
5. Check your default search engine
If your browser searches are being redirected somewhere unfamiliar, that’s classic adware and it maps back to items 1 through 3 above.
6. Run Apple’s own updates
System Settings → General → Software Update. Turn on automatic security responses. A lot of what people call “a virus” is actually a Mac that hasn’t been patched in two years.
Why “Mac cleaner” apps are usually the problem
This is the part nobody selling security software wants to say out loud. A large share of the “my Mac is infected” support requests trace back to a cleaner or optimizer app the person installed on purpose.
The pattern is consistent. The app is free to scan and paid to fix. The scan always finds hundreds of “issues”, which are mostly cache files, language packs, and log files that macOS manages fine on its own. It installs background helpers and sometimes a configuration profile. It nags you constantly with system-styled notifications. And uninstalling it properly is deliberately difficult.
None of that requires the app to be malicious in a legal sense. It just means the incentive is to make you anxious, and anxiety-driven software is a bad thing to give root access to.
macOS already has storage management built in: System Settings → General → Storage shows you what’s using space and offers to empty the trash automatically and offload unused files. The Recommendations there are honest, free, and won’t sell you a subscription. The same logic applies on phones, incidentally. You can usually free up storage without deleting anything using built-in tools rather than a third-party cleaner.
If you think you’re actually compromised
Assume credentials are the target, so treat this as a password problem, not a file problem.
Disconnect from Wi-Fi. Change the password on your Apple Account and your primary email from a different, trusted device. Those two accounts are the keys to everything else. Then work through anything financial. Sign out of all sessions everywhere, since stolen cookies let someone stay logged in without your password. Check for unfamiliar devices on your Apple Account. If you use a crypto wallet, move funds to a fresh one.
For the Mac itself: remove the suspicious login items, profiles and extensions, delete the app that started it, and restart. If you can’t get it clean, a wipe and reinstall from Apple’s recovery tools is faster and more certain than fighting it, and cheaper than any product that promises to do it for you.
FAQ
Do I need antivirus software on a Mac?
For most personal users, no. XProtect, Gatekeeper, notarization and SIP cover the realistic threats, and the main infection path in 2026 is a user manually approving something. Discipline about what you install does far more than a scanner. Managed workplace fleets are a different conversation, and that’s IT’s call, not yours.
Can a website really infect my Mac just by visiting?
Drive-by compromise through a browser bug is possible in principle and is exactly what Apple’s rapid security responses patch. In practice it’s rare and expensive to pull off, and it’s not what’s happening when a page shows you a virus warning. Keep Safari and macOS updated and you’ve addressed the realistic version of this risk.
I clicked the popup and something downloaded. Now what?
If you only downloaded it and never opened it, you’re fine: find it in your Downloads folder and delete it, then empty the trash. Infection requires you to run the installer and usually to type your admin password. If you did run it, work through the login items, profiles and extensions checks above, and change your important passwords from another device.
Is macOS still safer than Windows?
The picture’s more even than the old marketing suggested. macOS has a strong built-in security architecture, but it’s a valuable enough target now that dedicated malware families exist for it, and Windows has improved a lot. The honest version: on both platforms in 2026, the weakest link is the person approving the install. Your habits matter more than your operating system.
Same principle applies across your devices. A lot of “my phone is broken” turns out to be settings, not infection. If you’re moving between machines, our guide to transferring everything to a new phone covers doing it without dragging junk along for the ride.
I am the chief editor of TheLeaker. I also maintain the backend stuff of the site. I’m a tech enthusiast and loves to do Python coding in my free time. I have worked at many giant publications like XDA Developers and NXTtech before starting TheLeaker.
You can get in touch with me at Garv[at]theleaker.com.