You’ve probably been asked to “create a passkey” by Google, Amazon, PayPal or your bank in the last year. Most people tap Not now, because it sounds like one more thing to manage.
It’s actually one less thing. Passkeys are the first password replacement that’s genuinely simpler than a password, and Android has full support built in.
The quick answer: A passkey replaces your password with a cryptographic key stored on your phone and unlocked by your fingerprint, face or screen lock. There’s nothing to remember and nothing to type. To set one up, sign in to a site that supports passkeys, find the security or sign-in settings, and choose to create a passkey. Your phone prompts for your fingerprint and it’s done. On Android they’re stored in Google Password Manager by default and sync to any device signed into the same account, or you can use a third-party manager instead. Passkeys can’t be phished, can’t be reused across sites, and can’t be leaked in a data breach, because the site only ever stores a public key that’s useless on its own. Your password usually still exists as a fallback until you delete it.
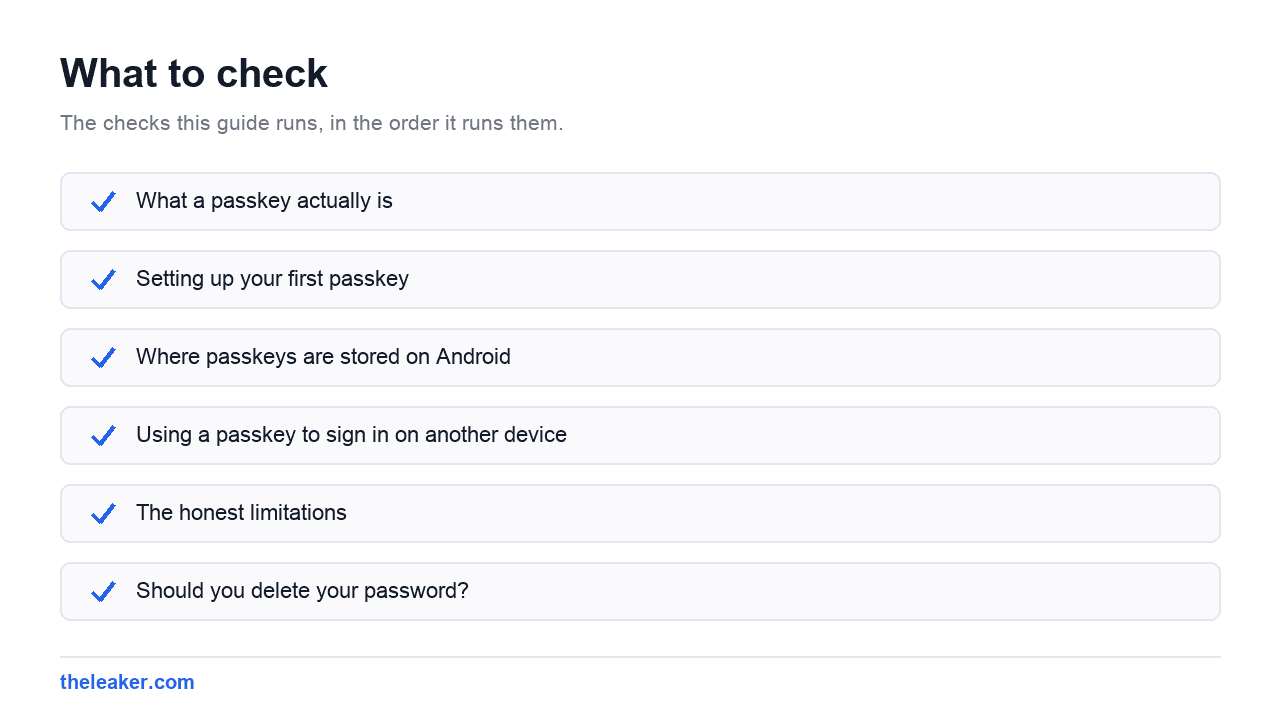
What a passkey actually is
Skip this if you don’t care about the mechanics, but it explains why passkeys are safer rather than just more convenient.
When you create a passkey, your phone generates a pair of mathematically linked keys. The private key never leaves your device’s secure hardware. The public key goes to the website.
When you sign in, the site sends a random challenge. Your phone signs it with the private key, but only after your fingerprint, face or PIN unlocks it. The site verifies the signature with the public key it already has. Nothing secret ever crosses the network.
Three consequences fall out of this:
- Breaches don’t matter. If the site gets hacked, attackers get public keys. Public keys are useless without the matching private key sitting in your phone’s security chip.
- Phishing doesn’t work. A passkey is bound to the exact domain it was created for. A fake site at a lookalike address simply won’t trigger your passkey, because the browser checks the domain before offering it. You can’t be tricked into handing it over. There’s nothing to hand over.
- Reuse is impossible. Every site gets a unique key pair. There’s no equivalent of using the same password in twelve places.
Your biometric data, incidentally, never goes anywhere. The fingerprint check happens entirely on your phone and just unlocks the key. Websites never see it.
Setting up your first passkey
Start with your Google account, because it’s the one that protects everything else on your phone.
- Go to
g.co/passkeysin a browser on your phone, or open your Google Account settings and find the Security section. - Look for Passkeys and security keys.
- Tap to create a passkey. You may need to re-enter your password to confirm it’s you.
- Your phone prompts for fingerprint, face or screen lock.
- Done. Next time you sign in to Google on that device, it’ll offer the passkey instead of a password.
The pattern is nearly identical everywhere else. Sign in normally, go to account or security settings, look for passkeys, create one, confirm with biometrics. Amazon, PayPal, eBay, X, LinkedIn, Best Buy, Adobe, Shopify, Nintendo, GitHub and a long and growing list of others support them.
Some sites will prompt you automatically right after you log in with a password. That’s the easiest moment to accept: say yes rather than Not now.
Where passkeys are stored on Android
By default, Google Password Manager. It’s built into Android, and passkeys stored there sync end-to-end encrypted to every device signed into the same Google account. Create a passkey on your phone, and your tablet and Chrome on your laptop can use it too.
Since Android 14, third-party password managers can act as passkey providers. If you already use 1Password, Bitwarden, Dashlane or similar, you can store passkeys there instead, which is worth doing if you’re not all-in on Google, or if you switch between Android and iPhone.
To change the default: open Settings, search for passkeys or autofill, and you’ll find a passwords and autofill section where you can pick your preferred provider. The exact path differs by phone. On Samsung’s One UI it’s under General management, and Samsung Pass sits alongside Google’s option as a competing provider: pick one and stick with it, because having both enabled causes confusing double prompts. Pixel keeps it under Passwords, passkeys and accounts. Xiaomi’s HyperOS and OnePlus bury it under additional or system settings but the same options are there.
Samsung Pass vs Google Password Manager
If you’re on a Galaxy, you’ve probably got both. Samsung Pass stores credentials in Samsung Knox and syncs across Samsung devices. Google Password Manager syncs across everything Google.
Neither is wrong. But if you ever plan to use a non-Samsung phone, Google’s option travels better. If you’re deep in the Samsung ecosystem and want credentials in Knox’s secure enclave, Samsung Pass is solid. Just don’t run both as passkey providers simultaneously.
Using a passkey to sign in on another device
This is where passkeys get clever. Say you’re on a friend’s laptop and need to log into your account.
On the sign-in page, choose to use a passkey from another device. A QR code appears. Scan it with your phone’s camera. Your phone asks for your fingerprint. You’re signed in on the laptop, and no passkey is copied to that laptop.
The two devices verify proximity over Bluetooth, which is a deliberate anti-phishing measure. A remote attacker can’t get you to scan a QR code from another continent, because the Bluetooth handshake would fail. Keep Bluetooth on for this to work.
The honest limitations
Passkeys are better than passwords. They are not without friction.
Support is incomplete. Plenty of major sites still don’t offer them. You’ll be running a hybrid setup (passkeys where available, passwords elsewhere) for years.
Recovery is tied to your account. If passkeys live in Google Password Manager and you lose access to your Google account, you lose the passkeys. Your Google account recovery becomes the single most important thing to secure. Keep recovery phone and email up to date, and consider keeping backup codes somewhere physical.
Losing your only device is awkward. If your passkeys sync, a new phone signed into the same account gets them back. If you used a device-bound passkey or a manager you can’t reach, you’re falling back to whatever recovery the site offers. Always have a second way in before you delete a password.
Cross-ecosystem is improving but clunky. Moving passkeys between Google, Apple and a third-party manager was historically impossible. Standards for importing and exporting have been developing, but don’t assume a smooth migration yet.
Shared accounts are messy. The family Netflix login that four people use doesn’t map neatly onto a credential bound to one person’s fingerprint. Some managers handle shared vaults; plenty of sites don’t cope.
Should you delete your password?
Not yet, in most cases. Having both means you’ve added a convenient, phishing-resistant way in without removing your safety net.
The counterargument is real though: if the password still exists, it can still be phished or breached. The passkey doesn’t protect you from someone stealing the password.
Reasonable middle ground: create passkeys everywhere you can, keep the passwords, but make sure those passwords are long, unique and stored in a manager. Once you’re confident in your recovery options and the site’s passkey implementation, remove the password on your highest-value accounts. Google, for instance, lets you skip passwords entirely once passkeys are set up.
Practical setup order
Do it in this sequence and you’ll never lock yourself out.
- Secure your screen lock first. A passkey is only as strong as the thing that unlocks it. A four-digit PIN is weak. Use six digits minimum, or a proper pattern plus biometrics.
- Sort out Google account recovery. Current phone number, current backup email, saved backup codes. This is now the master key.
- Create a passkey for your Google account.
- Add passkeys for financial and shopping accounts. The ones attackers actually target.
- Add them elsewhere as sites prompt you. Say yes instead of Not now.
- Keep a second device signed in where possible, so you’re never one broken phone away from a lockout.
If you’re setting this up as part of moving to a new handset, the sync behaviour matters: passkeys in Google Password Manager come across automatically once you sign in, but Samsung Pass entries won’t move to a non-Samsung device. Our guide on transferring everything to a new Android phone covers what carries over and what doesn’t.
Common confusions
“Passkeys are just biometric login.” No. Biometric login usually unlocks a stored password, which still gets sent to the site. A passkey means no password exists to send.
“My fingerprint gets uploaded.” Never. Biometrics stay in your phone’s secure hardware. They unlock the key locally.
“I need a new phone for this.” No. Passkeys work on Android 9 and later with a screen lock, and support has been broadly available for a few years now.
“It’s two-factor authentication.” Sort of, and better. A passkey combines something you have (the device) with something you are or know (biometric or PIN), in one step. On many sites, using a passkey satisfies 2FA requirements on its own.
Frequently asked questions
What happens to my passkeys if I lose my phone?
If they’re in Google Password Manager, they sync: sign into your Google account on a new phone and they come back. If they’re in a third-party manager, they come back when you sign into that manager. The real risk is losing access to whichever account holds them, which is why keeping your Google account recovery options current matters more than ever.
Are passkeys really safer than a strong password?
Yes, in ways a strong password can’t match. A passkey can’t be phished because it only works on the exact domain it was created for. It can’t be leaked in a breach because the site only stores a public key. And it can’t be reused, since every site gets its own key pair. A long unique password protects against reuse, but not phishing.
Can I use passkeys on both Android and iPhone?
Not seamlessly through the platform managers: Google Password Manager and Apple’s iCloud Keychain don’t sync to each other. The workaround is a cross-platform password manager like 1Password or Bitwarden as your passkey provider, which works on both. You can also use the QR code method to sign in on a device that doesn’t hold the passkey.
Do I still need my password after creating a passkey?
Usually the password stays as a fallback unless you explicitly delete it. Keeping it is sensible while you get comfortable, but it does mean the account can still be phished through the password. Once you’re confident in your recovery options, removing the password on high-value accounts closes that gap: Google, for example, lets you skip passwords entirely.
Where to start
Set one up on your Google account this week. It takes under two minutes, it’s the account everything else hangs off, and it’ll show you exactly how the flow feels. Then say yes the next time Amazon or PayPal offers. Within a few months you’ll have quietly replaced the logins you use daily, and typing a password will start to feel like an odd, old-fashioned thing to be asked to do.
Akshay Mhatre is a Tech Journalist who likes to keep up with the latest from the tech world. He has worked at many popular news portals like BGR and TechRadar before joining TheLeaker as a News writer and journalist. A writer by day and a VFX artist by night. In his free time, he also likes to make motion graphics and concept art. You can find him on Instagram @akshayrazr_95 and contact him on akshaymhatre[@]theleaker.com.